Important PHP Security Alert: What Happened?
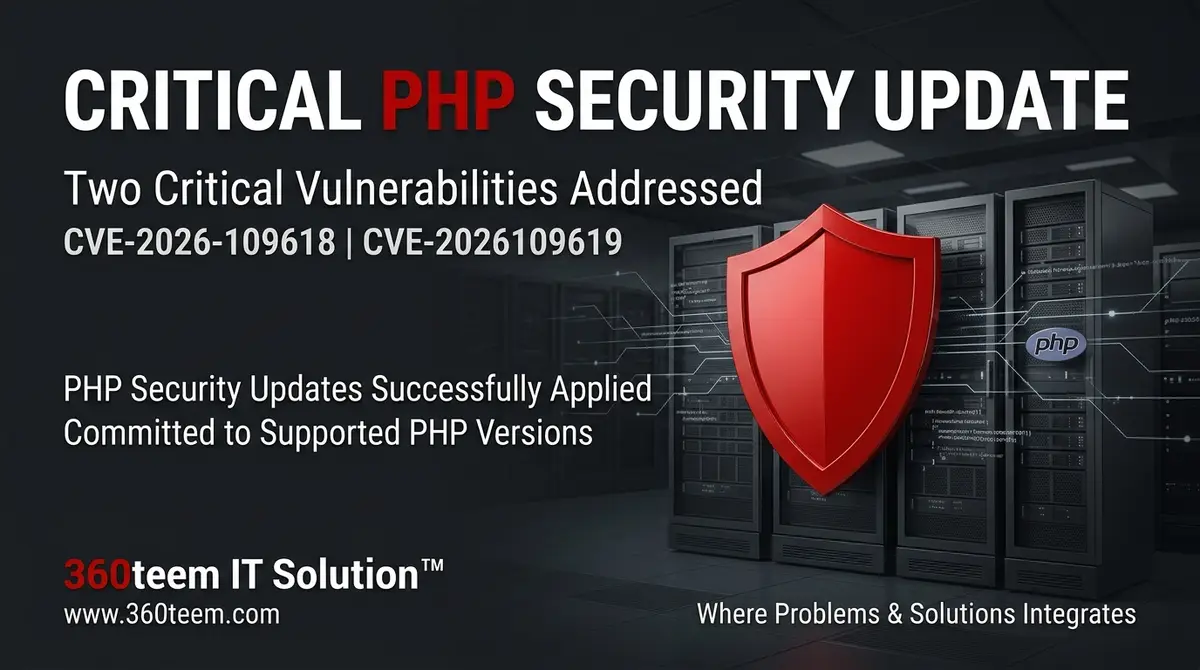
On 21 October 2026, the PHP development team released urgent security updates addressing two critical vulnerabilities that could allow attackers to execute malicious code remotely on vulnerable web servers, potentially without authentication.
The vulnerabilities are identified as:
CVE-2026-109618 — Remote Code Execution via Out-of-Memory Corruption: A memory-management failure could leave PHP’s internal request data in an inconsistent state, potentially allowing an attacker to exploit the affected process.
CVE-2026-109619 — Remote Code Execution via Stale Global State: Internal request-related state could remain accessible after its memory had been released, potentially allowing a later request to exploit the affected worker.
Both vulnerabilities received a CVSS v4.0 severity score of 9.2 out of 10. They may affect PHP installations serving web requests, including PHP-FPM, Apache mod_php, CGI-based deployments and LiteSpeed environments.
Successful exploitation could compromise the affected server and put website files, databases and other hosted resources at risk. The PHP security team released fixed versions on 21 October 2026, and strongly recommends immediate updates.
Official fixed releases: PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35.
Source: https://www.php.net/archive/2026.php
360teem IT Solution Has Updated Its Server PHP Versions
At 360teem IT Solution, protecting our clients’ websites and hosting infrastructure is a priority.
Following the latest PHP security advisory, we have successfully updated the PHP versions across our servers to address the reported security vulnerabilities.
Our objective is to ensure that our hosting infrastructure stays current with critical security patches and reduces exposure to known vulnerabilities.
Clients do not need to perform a PHP update at the server level themselves for this infrastructure-side remediation. However, application updates, compatible configurations and other website security measures remain important.
Our Policy on End-of-Life (EOL) PHP Versions
We are committed to moving away from PHP versions that have reached End of Life (EOL) and no longer receive security updates from the PHP project.
An EOL PHP version may continue to run, but new vulnerabilities discovered after its support period may remain unpatched unless a distribution or third-party vendor provides separate security maintenance.
The following PHP branches have reached official EOL, or are approaching it:
PHP version Official EOL date
PHP 5.6 31 December 2018
PHP 7.0 3 December 2018
PHP 7.1 1 December 2019
PHP 7.2 30 November 2020
PHP 7.3 6 December 2021
PHP 7.4 28 November 2022
PHP 8.0 26 November 2023
PHP 8.1 31 December 2025
PHP 8.2 31 December 2026 — upcoming
PHP 8.2 remains officially supported as of the publication date, but its security-support period ends on 31 December 2026. We encourage clients using older PHP branches to plan a migration to a supported version compatible with their website.
Official lifecycle information: https://www.php.net/supported-versions.php
What Does This Mean for Our Hosting Clients?
Our latest PHP security updates are an important step in protecting websites hosted on our infrastructure. We continue to prioritise security maintenance and the responsible management of supported PHP versions.
We recommend that clients also:
Keep WordPress, CMS platforms, plugins, themes and web applications updated.
Use supported PHP versions compatible with their applications.
Remove unused plugins, themes and extensions.
Maintain regular backups and use strong authentication.
Contact our support team if their website requires an older PHP version for compatibility.
Please note: Updating PHP helps address the vulnerabilities covered by the security releases, but no hosting environment or website can be guaranteed completely immune to every security threat. Application-level security and ongoing maintenance remain essential.
Our Commitment
At 360teem IT Solution, we believe reliable hosting means more than keeping a website online. It also means maintaining a responsible security posture, applying critical updates and planning ahead for unsupported software.
We will continue working to keep our server infrastructure updated and to reduce the risks associated with outdated software.
Your website matters to us. Security remains our priority.
For hosting assistance or PHP compatibility support, contact our team:
Website: https://www.360teem.com/
Email: contact@360teem.com
Support: +880-1912072147
360teem IT Solution™ — Where Problems & Solutions Integrates.
PHP-এর সর্বশেষ নিরাপত্তা সমস্যা: কী ঘটেছে?
২১ অক্টোবর ২০২৬ তারিখে PHP ডেভেলপমেন্ট টিম দুটি গুরুতর নিরাপত্তা দুর্বলতা সমাধানের জন্য জরুরি আপডেট প্রকাশ করেছে। এসব দুর্বলতা কাজে লাগিয়ে আক্রমণকারীরা আক্রান্ত ওয়েব সার্ভারে দূর থেকে ক্ষতিকর কোড চালাতে পারত, এমনকি কিছু পরিস্থিতিতে কোনো প্রমাণীকরণ ছাড়াই।
দুর্বলতা দুটি হলো:
CVE-2026-109618 — Out-of-Memory Corruption-এর মাধ্যমে Remote Code Execution: মেমোরি ব্যবস্থাপনায় ত্রুটির কারণে PHP-এর অভ্যন্তরীণ রিকোয়েস্ট ডেটা অসম্পূর্ণ বা অসংগত অবস্থায় থেকে যেতে পারত। নির্দিষ্ট পরিস্থিতিতে এটি কাজে লাগিয়ে আক্রমণ করা সম্ভব ছিল।
CVE-2026-109619 — Stale Global State-এর মাধ্যমে Remote Code Execution: মেমোরি মুক্ত করার পরও PHP-এর কিছু অভ্যন্তরীণ রিকোয়েস্ট-সম্পর্কিত অবস্থা থেকে যেতে পারত, যা পরবর্তী রিকোয়েস্ট প্রক্রিয়াকরণের সময় ঝুঁকি তৈরি করতে পারত।
উভয় দুর্বলতার CVSS v4.0 ঝুঁকির স্কোর ১০-এর মধ্যে ৯.২। PHP-FPM, Apache mod_php, CGI এবং LiteSpeed-এর মতো ওয়েব রিকোয়েস্ট পরিচালনাকারী পরিবেশগুলো এর আওতায় আসতে পারে।
এই দুর্বলতাগুলো সফলভাবে কাজে লাগানো হলে আক্রান্ত সার্ভার, ওয়েবসাইটের ফাইল, ডেটাবেজ এবং অন্যান্য হোস্ট করা রিসোর্স ঝুঁকির মুখে পড়তে পারে।
PHP কর্তৃপক্ষ ২১ অক্টোবর ২০২৬ তারিখে নিরাপত্তা আপডেট প্রকাশ করেছে।
নিরাপত্তা সংশোধনসহ প্রকাশিত সংস্করণ: PHP 8.5.12, 8.4.27, 8.3.36 এবং 8.2.35।
অফিশিয়াল সূত্র: https://www.php.net/archive/2026.php
360teem IT Solution-এর সার্ভারে PHP নিরাপত্তা আপডেট সম্পন্ন
আমাদের গ্রাহকদের ওয়েবসাইট এবং হোস্টিং অবকাঠামোর নিরাপত্তা নিশ্চিত করা 360teem IT Solution-এর অন্যতম অগ্রাধিকার।
সর্বশেষ PHP নিরাপত্তা সতর্কতা প্রকাশের পর আমরা আমাদের সার্ভারগুলোতে ব্যবহৃত PHP সংস্করণগুলোর প্রয়োজনীয় আপডেট সফলভাবে সম্পন্ন করেছি, যাতে প্রকাশিত নিরাপত্তা দুর্বলতাগুলোর বিরুদ্ধে সুরক্ষা জোরদার করা যায়।
আমাদের লক্ষ্য হলো নিয়মিত গুরুত্বপূর্ণ নিরাপত্তা আপডেট প্রয়োগ করা এবং পরিচিত দুর্বলতার কারণে সার্ভার ও ওয়েবসাইটের ঝুঁকি কমিয়ে রাখা।
এই সার্ভার-পর্যায়ের আপডেটের জন্য গ্রাহকদের নিজেদের ওয়েবসাইটের সার্ভারে PHP আপডেট করার প্রয়োজন নেই। তবে ওয়েবসাইটের CMS, প্লাগইন, থিম, অ্যাপ্লিকেশন এবং অন্যান্য নিরাপত্তা ব্যবস্থা নিয়মিত আপডেট রাখা জরুরি।
EOL PHP সংস্করণ আর ব্যবহার না করার নীতি
আমরা এমন PHP সংস্করণ থেকে সরে আসার নীতি অনুসরণ করছি, যেগুলো End of Life (EOL) পর্যায়ে পৌঁছেছে এবং PHP প্রকল্প থেকে আর নিয়মিত নিরাপত্তা আপডেট পায় না।
EOL সংস্করণে তৈরি ওয়েবসাইট চলতে পারে, কিন্তু পরবর্তীতে নতুন নিরাপত্তা দুর্বলতা শনাক্ত হলে সেগুলোর জন্য PHP প্রকল্প থেকে আর সংশোধনী নাও পাওয়া যেতে পারে। কোনো অপারেটিং সিস্টেম বা তৃতীয় পক্ষ আলাদাভাবে নিরাপত্তা সহায়তা দিলে পরিস্থিতি ভিন্ন হতে পারে।
নিচে বহুল পরিচিত পুরোনো PHP সংস্করণগুলোর EOL তারিখ দেওয়া হলো:
PHP সংস্করণ অফিসিয়াল EOL তারিখ
PHP 5.6 ৩১ ডিসেম্বর ২০১৮
PHP 7.0 ৩ ডিসেম্বর ২০১৮
PHP 7.1 ১ ডিসেম্বর ২০১৯
PHP 7.2 ৩০ নভেম্বর ২০২০
PHP 7.3 ৬ ডিসেম্বর ২০২১
PHP 7.4 ২৮ নভেম্বর ২০২২
PHP 8.0 ২৬ নভেম্বর ২০২৩
PHP 8.1 ৩১ ডিসেম্বর ২০২৫
PHP 8.2 ৩১ ডিসেম্বর ২০২৬ — আসন্ন
প্রকাশের তারিখ অনুযায়ী PHP 8.2 এখনো অফিসিয়াল নিরাপত্তা সহায়তার আওতায় রয়েছে। তবে এর নিরাপত্তা সহায়তা ৩১ ডিসেম্বর ২০২৬-এ শেষ হবে। পুরোনো সংস্করণ ব্যবহারকারীদের নিজস্ব ওয়েবসাইটের সঙ্গে সামঞ্জস্যপূর্ণ, সমর্থিত PHP সংস্করণে যাওয়ার পরিকল্পনা করার পরামর্শ দিচ্ছি।
PHP-এর অফিসিয়াল লাইফসাইকেল: https://www.php.net/supported-versions.php
আমাদের হোস্টিং গ্রাহকদের জন্য এর অর্থ কী?
সর্বশেষ PHP নিরাপত্তা আপডেট আমাদের হোস্টিং অবকাঠামোয় পরিচালিত ওয়েবসাইটগুলোর সুরক্ষা জোরদার করার একটি গুরুত্বপূর্ণ পদক্ষেপ। আমরা নিয়মিত নিরাপত্তা রক্ষণাবেক্ষণ এবং সমর্থিত PHP সংস্করণ ব্যবস্থাপনায় গুরুত্ব দিয়ে থাকি।
পাশাপাশি গ্রাহকদের প্রতি আমাদের পরামর্শ:
WordPress, CMS, প্লাগইন, থিম এবং ওয়েব অ্যাপ্লিকেশন নিয়মিত আপডেট রাখুন।
ওয়েবসাইটের সঙ্গে সামঞ্জস্যপূর্ণ সমর্থিত PHP সংস্করণ ব্যবহার করুন।
অব্যবহৃত প্লাগইন, থিম ও এক্সটেনশন সরিয়ে ফেলুন।
নিয়মিত ব্যাকআপ রাখুন এবং শক্তিশালী লগইন নিরাপত্তা ব্যবহার করুন।
সামঞ্জস্যের কারণে পুরোনো PHP সংস্করণ প্রয়োজন হলে আমাদের সাপোর্ট টিমের সঙ্গে যোগাযোগ করুন।
মনে রাখবেন: PHP আপডেট সংশ্লিষ্ট নিরাপত্তা দুর্বলতাগুলোর ঝুঁকি কমাতে সাহায্য করে। তবে শুধু PHP আপডেট করলেই কোনো ওয়েবসাইট সব ধরনের সাইবার আক্রমণ থেকে সম্পূর্ণ নিরাপদ হয়ে যায় না। অ্যাপ্লিকেশন নিরাপত্তা, নিয়মিত রক্ষণাবেক্ষণ এবং অন্যান্য সুরক্ষা ব্যবস্থাও গুরুত্বপূর্ণ।
নিরাপদ হোস্টিংয়ের প্রতি আমাদের অঙ্গীকার
360teem IT Solution-এর কাছে নির্ভরযোগ্য হোস্টিং মানে শুধু ওয়েবসাইট সচল রাখা নয়। এর অর্থ হলো নিরাপত্তার দায়িত্বশীল ব্যবস্থাপনা, গুরুত্বপূর্ণ আপডেট প্রয়োগ এবং মেয়াদোত্তীর্ণ সফটওয়্যার এড়িয়ে চলা।
আমরা আমাদের সার্ভার অবকাঠামো নিয়মিত আপডেট রাখতে এবং পুরোনো সফটওয়্যার থেকে সৃষ্ট ঝুঁকি কমাতে কাজ করে যাব।
আপনার ওয়েবসাইট আমাদের কাছে গুরুত্বপূর্ণ। আপনার নিরাপত্তাই আমাদের অগ্রাধিকার।